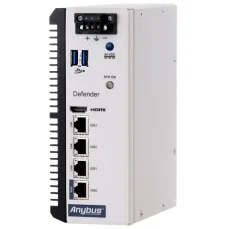
New to the market: Anybus Defender industrial firewalls for OT network security and segmentation
Anybus Defender industrial firewalls help segment OT networks, resolve IP conflicts, inspect traffic with DPI and support compliance with IEC 62443 and the NIS2 Directive. They help protect critical infrastructure and production technology, reduce the risk of unplanned downtime and address cybersecurity risks without disrupting operations.
Why does your OT network need a dedicated firewall?
Conventional IT firewalls can fall short in manufacturing environments because they may not understand industrial protocols and can be unnecessarily complex to manage. Anybus Defender supports both physical and logical segmentation. It lets you separate individual machines, cells or production lines and strictly allow only the communication required for operation.
What can Anybus Defender help you address?
These devices can help reduce cybersecurity risks and support compliance with relevant requirements, including:
Network segmentation in accordance with IEC/ISA 62443-3-3
Identical IP address conflicts on duplicate machines, resolved with advanced NAT
Requirements of the NIS2 Directive
Protection of vulnerable and legacy devices (legacy PLCs) against unwanted interference and attacks
Three levels of protection: NAT/FW, DPI/FW and PRO/FW
Anybus offers firewalls in three functional variants, so you can choose the one that fits your needs:
NAT/FW (basic protection): Ideal for separating networks, allowing selected traffic, routing and resolving IP conflicts with Network Address Translation (NAT).
DPI/FW (advanced protection): Includes all NAT/FW features and adds Deep Packet Inspection (DPI) for in-depth inspection of common industrial protocols, an intrusion detection and prevention system (IDS/IPS), protection for vulnerable devices and VPN.
PRO/FW (advanced networking features): Includes all DPI/FW features and adds a VPN server and client for OT-SDWAN, advanced routing, Multi-WAN and high availability.
Managing multiple devices centrally
The Anybus Cybersecurity Console (ACC) is used to manage multiple Anybus Defender devices. It provides a unified overview of the entire network from one place. You can deploy security rules and user groups in bulk and configure devices quickly without interrupting production or taking the system offline.
Not sure which type is right for you? We’ll help.
Browse the available models in the Cybersecurity – OT Network Security category.