

Anybus Defender 6004 - License type: NAT/FW

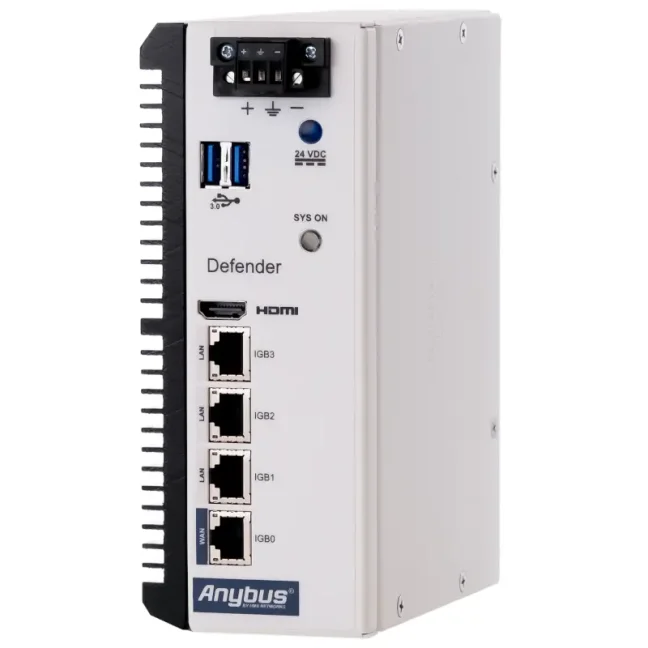
Industrial firewall and security router for isolating and protecting machines, production lines, and other parts of the OT network. It provides 1× WAN and 3× LAN Gigabit ports, VLAN support, NAT, bridge operation, and configuration via a web interface. Available in 3 variants: NAT/FW for network isolation and IP address translation, DPI/FW with industrial protocol inspection and virtual protection against known vulnerabilities, or PRO/FW with advanced VPN, routing, traffic management, and high-availability functions. More
Code: ABD6004-NATFW
Options 3
| License type | Code | Availability | Price excl. VAT | |
|---|---|---|---|---|
| NAT/FW | ABD6004-NATFW | Delivery in 1-2 weeks |
2 030 EUR
|
|
| DPI/FW | ABD6004-DPIFW | Delivery in 1-2 weeks |
2 682 EUR
|
|
| PRO/FW | ABD6004-PROFW | Delivery in 1-2 weeks |
4 930 EUR
|
Anybus Defender 6004
Anybus Defender 6004 is an industrial firewall for isolating and securing machines, production lines, and other parts of the OT network. It helps restrict unwanted communication, resolve IP address conflicts, and protect connected devices when communicating with the production or enterprise network. Depending on the selected variant, it also provides industrial protocol inspection, protection of vulnerable devices without requiring updates, VPN, and advanced networking features.
Why choose Anybus Defender 6004?
- Connects up to four physical network segments – 1× WAN and 3× independently configurable LAN ports allow multiple parts of the system to be isolated using a single device.
- Reduces the risk of problems spreading through the network – individual machines, lines, or production areas can be separated from one another and only the required communication can be allowed between them.
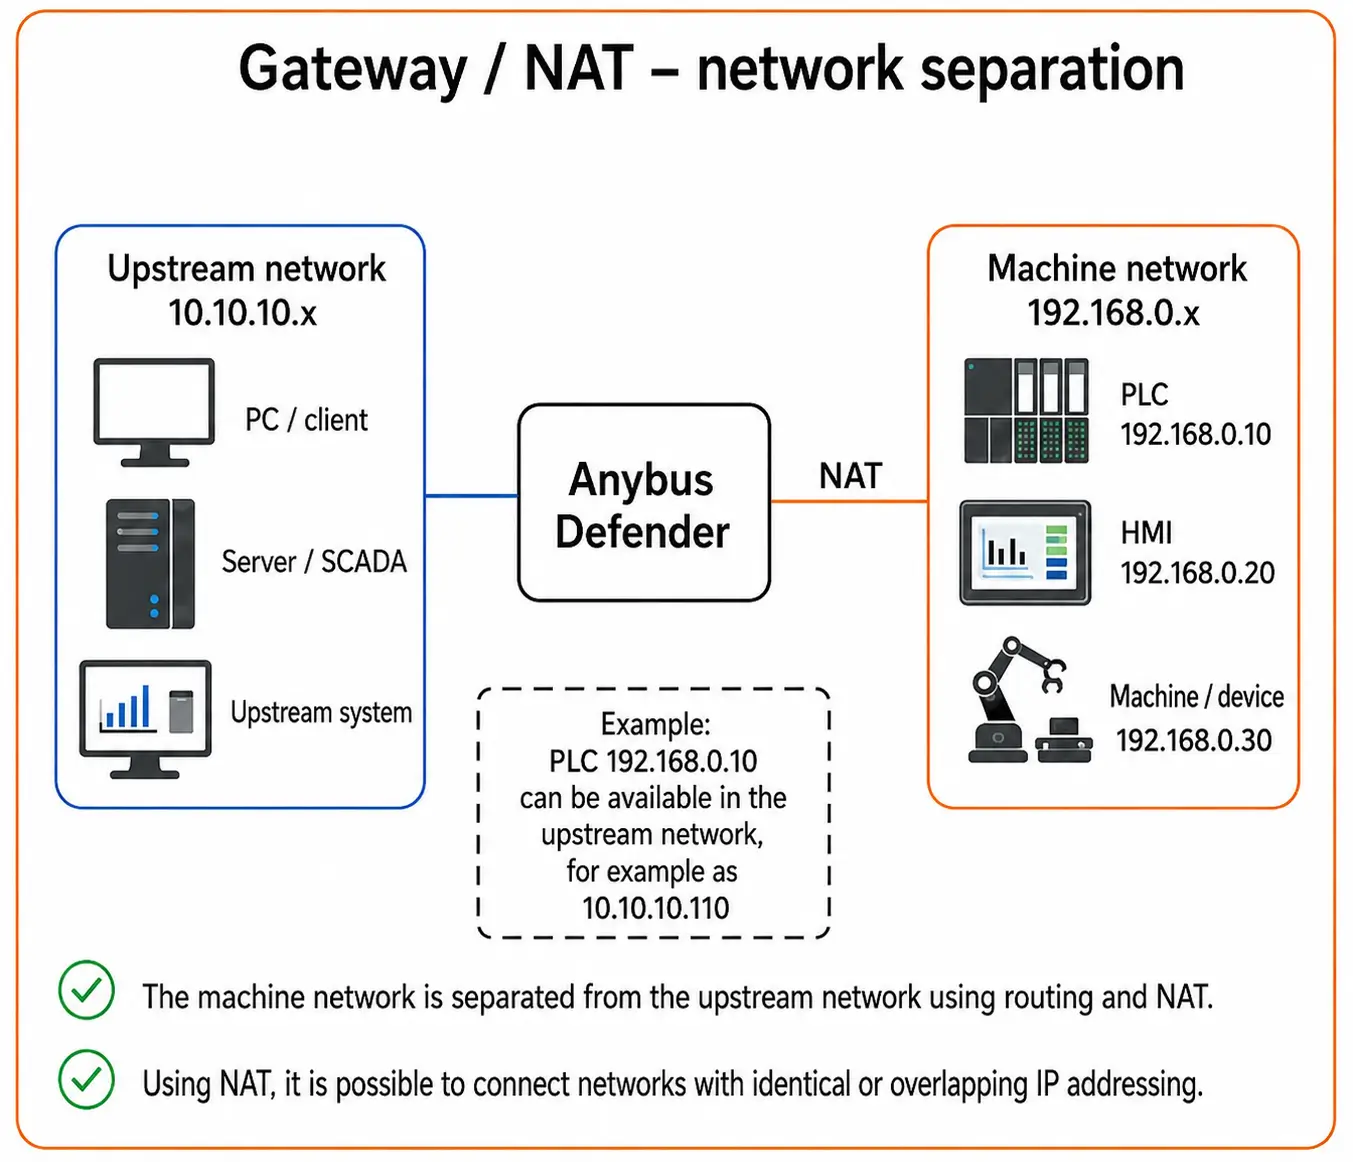
- Makes it easier to connect identical machines – NAT allows systems with identical internal IP addresses to be connected without changing their configuration.
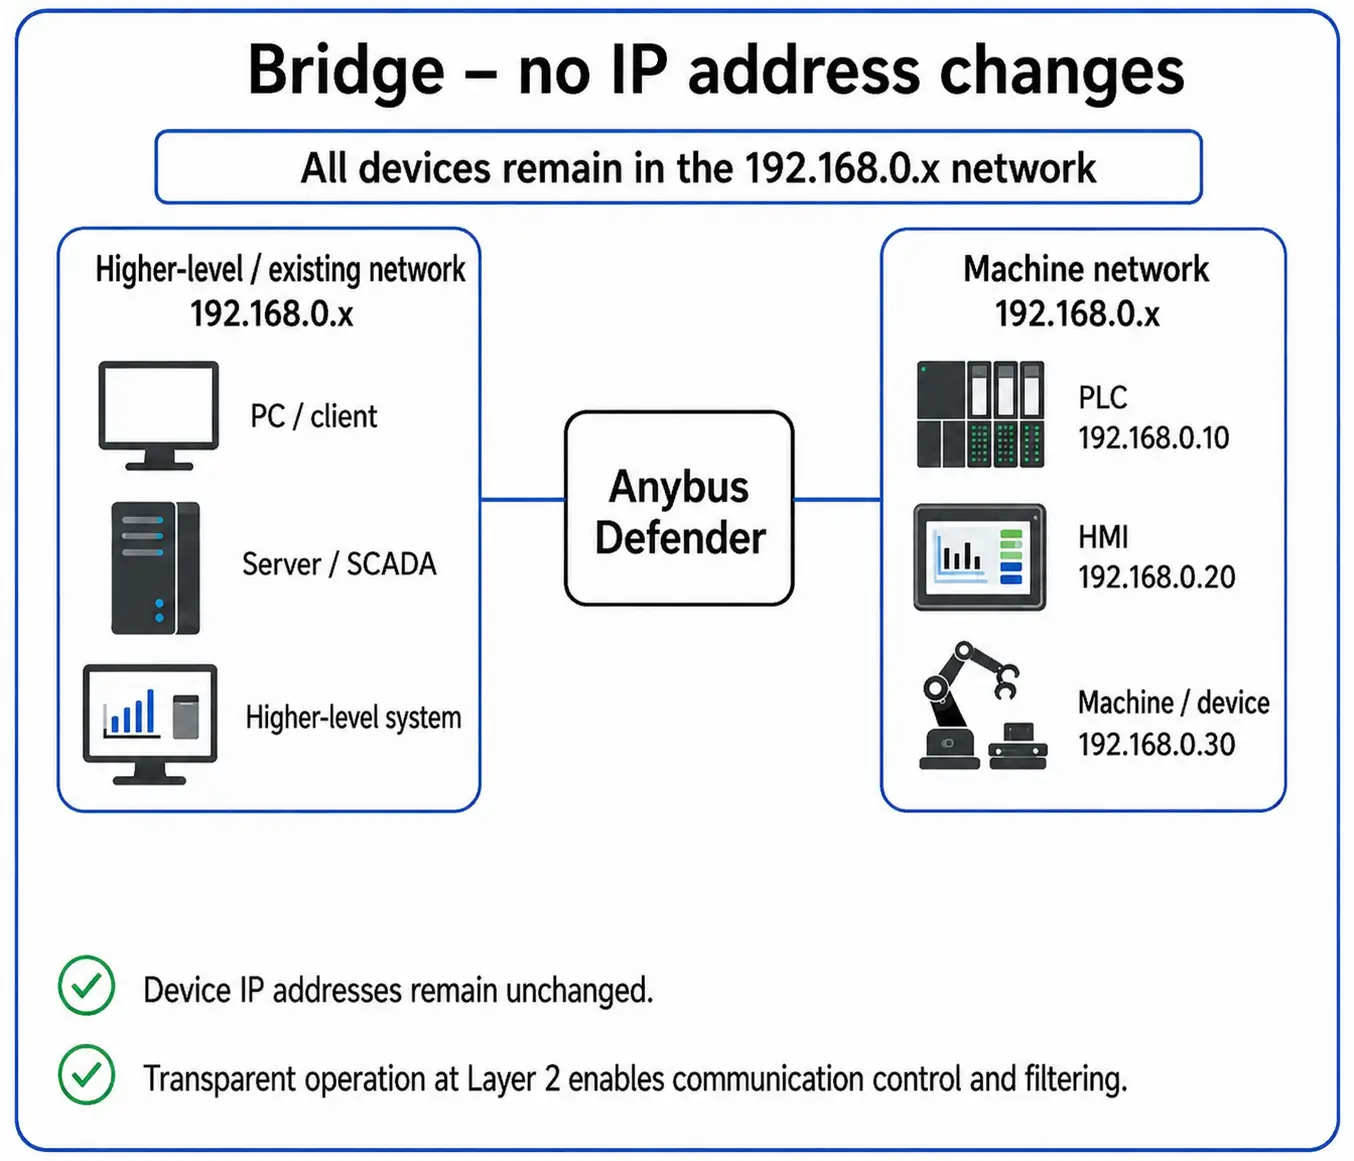
- Can be added to an existing network – in a bridge configuration, it controls communication without changing the IP addresses of PLCs, HMIs, and other devices.
- Provides visibility of connected devices – the Asset Discovery & Inventory feature helps identify devices in the OT network.
- Simplifies firewall configuration – configuration is performed through a web interface with wizards, and rules can be created directly from recorded communication.
- Can be adapted to the required level of protection – NAT/FW, DPI/FW, and PRO/FW variants are available with the same hardware but different feature sets.
Anybus Defender 6004 variants
Anybus Defender 6004 is available in three variants with the same hardware but different ranges of security and networking features:
- NAT/FW – basic protection for network isolation, communication control, and IP address translation,
- DPI/FW – all NAT/FW features + industrial communication inspection, IPS, protection of vulnerable devices without requiring updates, and VPN,
- PRO/FW – all DPI/FW features + advanced routing, network traffic management, and high availability.
Comparison of Anybus Defender variants
| Feature / what it solves | NAT/FW Basic protection and network isolation |
DPI/FW Advanced industrial network protection |
PRO/FW Advanced networking features and high availability |
|---|---|---|---|
| Connecting networks with different or identical IP addresses (NAT 1:1, 1:∞) | ✔ | ✔ | ✔ |
| Firewall with connection state tracking (Stateful Firewall) | ✔ | ✔ | ✔ |
| Network protection without changing IP addresses (Transparent / Bridge Mode) | ✔ | ✔ | ✔ |
| Security certificate management (Certificate Management) | ✔ | ✔ | ✔ |
| Central management of multiple Defenders (Anybus Cybersecurity Console) | ✔ | ✔ | ✔ |
| Automatic discovery and inventory of network devices (Asset Discovery & Inventory) | ✔ | ✔ | ✔ |
| Event notifications by email, Syslog, Telegram, and Pushover | ✔ | ✔ | ✔ |
| Secure remote user connection via VPN (Remote Client VPN) | — | ✔ | ✔ |
| User authentication via corporate accounts (RADIUS, LDAP / Active Directory) | — | ✔ | ✔ |
| Industrial communication inspection and easier rule creation (DPI for EtherNet/IP CIP, Siemens TCP/IP, and Modbus) | — | ✔ | ✔ |
| Protection of vulnerable and legacy devices against known attacks without requiring updates (IPS / Virtual Patching – Snort, Suricata) | — | ✔ | ✔ |
| Connecting networks through secure VPN tunnels (WireGuard, OpenSSL, IPsec) | — | ✔ | ✔ |
| Automatic IP address assignment and forwarding of DHCP requests (DHCP Server / Forwarding) | — | ✔ | ✔ |
| Enabling and disabling rules based on time (Rules / Policy Scheduler) | — | ✔ | ✔ |
| Login page for granting network access (Captive Portal) | — | — | ✔ |
| Advanced automatic routing between networks (RIP, BGP) | — | — | ✔ |
| Multiple network or internet connections and traffic distribution between them (Load Balancing, Multi-WAN) | — | — | ✔ |
| Management of network traffic priority and bandwidth (Traffic Shaping) | — | — | ✔ |
| Backup firewall to reduce downtime in case of failure (High Availability Redundancy) | — | — | ✔ |
Anybus Defender 6004 NAT/FW
The NAT/FW variant is designed for isolating machines and production networks, controlling permitted communication, and resolving IP address conflicts. Thanks to three independently configurable LAN ports, a single Defender can isolate multiple physical network segments.
It includes a stateful firewall, NAT, transparent bridge operation, certificate management, Asset Discovery & Inventory, and support for central management.
Typical applications include isolating several machines or production cells from the higher-level network, creating a controlled connection between OT and IT, or connecting multiple systems with identical or overlapping IP addresses.
Anybus Defender 6004 DPI/FW
The DPI/FW variant includes all NAT/FW features and extends them with detailed inspection of the industrial protocols EtherNet/IP CIP, Siemens TCP/IP, and Modbus. The firewall therefore evaluates not only IP addresses and ports, but can also inspect the industrial communication itself.
The integrated traffic analyzer with automatic learning helps identify the industrial communication being used and simplifies the creation of corresponding rules. The Snort and Suricata IPS systems can detect known threats and protect, for example, legacy PLCs, HMIs, and other vulnerable devices without requiring a patch to be installed directly on the device (Virtual Patching).
DPI/FW also supports remote VPN access, secure VPN tunnels using WireGuard, OpenSSL, and IPsec, user authentication via RADIUS and LDAP / Active Directory, DHCP server and DHCP request forwarding, and time-based rule scheduling.
The DPI/FW variant is suitable where network isolation and standard communication filtering alone are not sufficient and more detailed inspection of industrial traffic, protection of vulnerable devices, or secure remote access is also required.
Anybus Defender 6004 PRO/FW
The PRO/FW variant includes all DPI/FW features and extends them with advanced routing, network traffic management, and high availability.
It supports the RIPv1, RIPv2, and BGPv4 routing protocols, Load Balancing, Multi-WAN, and Traffic Shaping. This makes it possible to manage data paths, the use of multiple network connections, bandwidth, and network traffic priority.
The PRO/FW variant also includes a Captive Portal, which can require users to log in before access to the protected network is granted.
Two devices can be configured in active-standby high-availability mode. If the active unit fails, the backup Defender can take over its function, reducing the risk of interruption to critical network communication.
The PRO/FW variant is suitable for larger production networks, applications with multiple network connections, and environments with higher requirements for availability, routing, and network traffic management.
Not sure which Defender to choose?
Tell us about your network and what you need to secure. We will recommend the right model and variant.
Consult your Defender selection
Isolation of multiple physical and logical networks
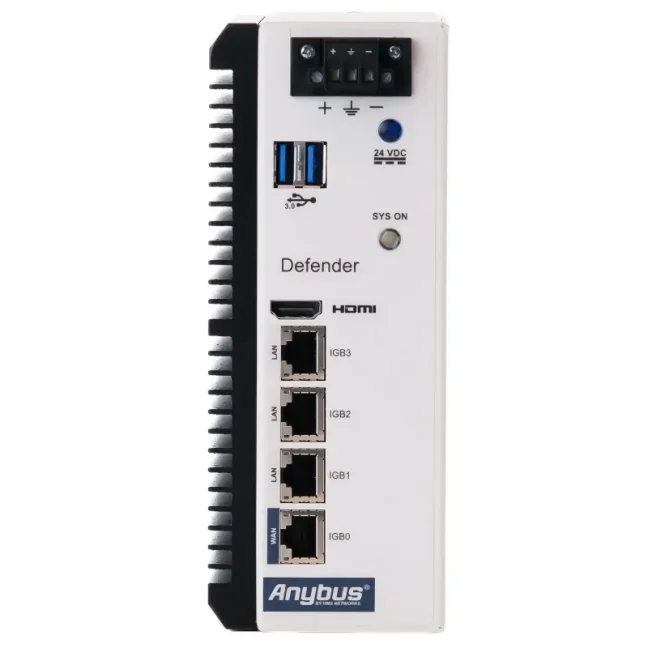
Anybus Defender 6004 is equipped with one Gigabit WAN port and three Gigabit LAN ports. The three independently configurable LAN ports make it possible to connect and isolate several machines, production cells, or other network segments without requiring an additional router or firewall.
Each interface can have its own communication rules. Individual parts of the system can therefore communicate with the higher-level network or with one another only within the permitted scope. VLAN support allows additional logically isolated networks to be created on the physical interfaces.
Defender 6004 is therefore suitable, for example, for isolating several production cells, service networks, data acquisition systems, or other parts of the OT infrastructure. For suitable applications, one of the LAN ports can also be configured as a second WAN port.
A firewall that allows only the required communication
All communication between connected networks passes through the stateful firewall. The Defender uses the principle “what is not allowed is denied”, so network communication is blocked unless it is explicitly permitted by configured rules.
For example, a PLC can be allowed to communicate only with a specific service computer, production data can be made available to a SCADA or MES system, while access to other parts of the production network remains blocked. Rules can be configured for individual interfaces or as common rules that apply to multiple interfaces.
Two connection modes
Bridge – without changing IP addresses
In a bridge configuration, the Defender can be added to an existing network connection without changing the IP addresses of connected devices. PLCs, HMIs, robots, drives, and other devices retain their original settings, while their communication starts passing through the firewall.
This configuration is particularly suitable for retrofitting security to an existing machine or production line where changing the network configuration would require a complex intervention or production downtime.
Gateway – network isolation and NAT
In a gateway configuration, the Defender operates as a router between isolated networks. Individual segments can use different IP address ranges, and communication between them is controlled using routing, NAT, and firewall rules.
NAT, or Network Address Translation, makes it possible to keep the original IP addresses inside the machine while communicating with the devices from the higher-level network using translated addresses. This is particularly useful when connecting multiple identical machines with the same internal IP addressing.
 |
 |
Visibility of devices in the OT network
The Asset Discovery & Inventory feature discovers devices in connected networks and, depending on the available information, can identify details such as their manufacturer, type, software version, update level, or serial number.
This helps provide an overview of the devices actually connected to the network and identify unknown or unexpected elements. The result also includes an identification confidence rating. The feature is available in all Defender 6004 variants.
Web interface and diagnostics
Configuration is performed through the integrated web interface directly in a web browser. Wizards are available for common connection scenarios and for configuring network and security features.
Rules can also be created directly from communication recorded in the firewall logs. The One-Click Easy Rule feature makes it easier to create the rules required for system operation. Common rules that can be applied across multiple interfaces are also available.
Diagnostic tools and network traffic analysis tools are included. A REST API is available for integration with higher-level systems, while maintenance can also be performed through the CLI via SSH or a local console. Multiple devices can optionally be managed using the central Anybus Cybersecurity Console.
Online documentation
Online documentation from the manufacturer is available for configuring and working with Anybus Defender features. It contains information on installation, firewall configuration, NAT, DPI, VPN, routing, and other functions depending on the specific model and variant.
Technical specifications
Network interfaces and connection
- WAN: 1× RJ45, Gigabit Ethernet
- LAN: 3× RJ45, Gigabit Ethernet
- Port configuration: LAN ports are independently configurable; one of them can be configured as a second WAN port for suitable applications
- Number of physical network segments: up to 4
- VLAN: yes, allows multiple logically isolated network segments to be created
- Bridge: transparent integration into an existing network without changing the IP addresses of connected devices
- Gateway: network isolation using routing, NAT, and firewall rules
- Supported network protocols: IPv4 and IPv6
NAT and IP address translation
- NAT: translation of individual IP addresses, multiple addresses, or entire subnets
- Simple NAT Wizard: support for configuring 1:1 and 1:∞ NAT
- Transparent filtering: Layer 2 communication filtering in a bridge configuration
Firewall and communication filtering
- Firewall type: stateful firewall
- Default security policy: communication is denied until explicitly permitted
- Filtering direction: inbound and outbound communication
- One-Click Easy Rule: creates a rule directly from communication recorded in the firewall logs
- Floating Rules: common rules that can be applied across multiple interfaces
- Application and URL whitelist: yes
Device discovery in the OT network
- Feature: Asset Discovery & Inventory
- Purpose: discovery and identification of devices connected to the OT network
- Detected information: depending on availability, manufacturer, device type, software version, update level, and serial number
- Output: overview of discovered devices including an identification confidence rating
- Availability: NAT/FW, DPI/FW, and PRO/FW
Configuration and management
- Configuration: integrated web interface accessible through a web browser
- Setup wizards: yes, for common connection and configuration scenarios
- Diagnostics: firewall logs, network communication diagnostics, and traffic analysis tools
- Advanced management: command line via SSH or local console
- REST API: yes, for integration with higher-level systems
- Central management: optionally via Anybus Cybersecurity Console
- Certificate management: yes
Monitoring and notifications
- Notifications: email, Syslog, Telegram Messenger, and Pushover
- Monitoring: ARP and bandwidth utilization monitoring via API
- NetFlow: optional integration
NAT/FW variant features
- Stateful firewall: yes
- NAT: yes
- Transparent bridge operation: yes
- Asset Discovery & Inventory: yes
- Certificate management: yes
- Central management: support for the optional Anybus Cybersecurity Console
Extended features of the DPI/FW and PRO/FW variants
- Deep Packet Inspection (DPI): detailed inspection of supported industrial protocols
- Supported DPI protocols: EtherNet/IP CIP, Siemens TCP/IP, and Modbus
- Automatic traffic learning: analysis of industrial communication to simplify rule creation
- IPS: Snort and Suricata
- Customizable IPS signatures: yes
- Virtual patching: protection of devices against known methods of exploiting vulnerabilities
- VPN: WireGuard, OpenSSL, and IPsec
- Remote Client VPN: yes
- User authentication: RADIUS and LDAP/Active Directory
- DHCP: DHCP server and DHCP forwarding
- Rule scheduling: by date, time, and duration
Extended features of the PRO/FW variant
- Captive Portal: login page before network access is granted
- Routing protocols: RIPv1, RIPv2, and BGPv4
- Load Balancing: yes
- Multi-WAN: yes
- Traffic Shaping: network traffic management and prioritization
- High availability: redundant configuration of two devices in active-standby mode
Power supply
- Supply voltage: 24 VDC
- Maximum current consumption: 1,100 mA at 24 VDC
- Maximum power consumption: 26.4 W
Mechanical and operating specifications
- Dimensions (H × W × D): 179.7 × 69.6 × 146 mm
- Weight: 1,270 g
- Enclosure material: metal
- Cooling: passive, fanless
- Degree of protection: IP20
- Operating temperature: 0 to +50 °C at full CPU load, up to +60 °C under typical load
- Relative humidity: 0–85%, non-condensing
- Mounting: DIN rail according to EN 50022
Certifications and compliance
- Certifications and compliance: CE, RoHS, WEEE, RCM, UKCA, and EMC
Frequently Asked Questions (FAQ) – Anybus Defender 6004
Use and network connection
What is Anybus Defender 6004 and what is it used for?
Anybus Defender 6004 is an industrial firewall and security router for isolating and protecting machines, production lines, and other parts of the OT network. It is used to control communication between networks, resolve IP address conflicts, and limit the spread of security incidents.
What is an industrial firewall used for in a production network?
An industrial firewall isolates and protects machines, production lines, and other parts of the OT network. Anybus Defender 6004 allows communication between networks to be controlled, IP address conflicts to be resolved, and the spread of security incidents to be limited.
How can I isolate several machines or parts of a production network with one firewall?
Anybus Defender 6004 has one WAN port and three independently configurable LAN ports. This allows several machines, production cells, or other network segments to be isolated. VLANs can also be used to create additional logically isolated networks.
How can I isolate machines from the enterprise network and allow only the required communication?
Anybus Defender 6004 is installed between the protected production areas and the higher-level network. Its stateful firewall uses the principle “what is not allowed is denied,” so communication is blocked unless it is explicitly permitted by configured rules.
How can I secure an operating machine without changing its IP addresses?
Anybus Defender 6004 can be inserted into an existing network connection in a bridge configuration without changing the IP addresses of PLCs, HMIs, and other devices. The original addressing remains unchanged while communication starts passing through the firewall.
What is the difference between bridge and gateway configurations on an industrial firewall?
In a bridge configuration, Anybus Defender 6004 transparently controls communication without changing the IP addresses of connected devices. In a gateway configuration, Anybus Defender 6004 separates individual networks and allows routing, NAT, and firewall rules to be used.
Selecting a variant according to the application
What is the difference between the NAT/FW, DPI/FW, and PRO/FW variants?
The Anybus Defender 6004 NAT/FW variant provides a stateful firewall, NAT, and network isolation. Anybus Defender 6004 DPI/FW adds industrial protocol inspection, IPS, virtual patching, and other security features. Anybus Defender 6004 PRO/FW additionally provides advanced VPN, routing, network traffic management, and high availability.
How can I connect several identical machines with the same IP addresses to one network?
Anybus Defender 6004 uses NAT to keep the original IP addresses inside individual machines while communicating with the devices from the higher-level network using translated addresses. For this type of application, the Anybus Defender 6004 NAT/FW variant is usually sufficient.
How can I inspect industrial communication in more detail than just by IP addresses and ports?
The Anybus Defender 6004 DPI/FW and Anybus Defender 6004 PRO/FW variants support Deep Packet Inspection for the industrial protocols EtherNet/IP CIP, Siemens TCP/IP, and Modbus. The firewall can therefore control communication based on the content of supported industrial protocols as well.
How can I protect older PLCs or HMIs that can no longer be updated?
The Anybus Defender 6004 DPI/FW and Anybus Defender 6004 PRO/FW variants include Snort and Suricata IPS and support virtual patching. Anybus Defender can therefore help block known methods of exploiting vulnerabilities before they reach the protected device.
When should I choose PRO/FW instead of NAT/FW or DPI/FW?
Anybus Defender 6004 PRO/FW is suitable where, in addition to advanced security, VPN and functions for larger network infrastructures are also required, such as the RIPv1, RIPv2, and BGPv4 routing protocols, Load Balancing, Multi-WAN, Traffic Shaping, or high availability.
Firewall, NAT, and network visibility
How does the firewall decide which communication between production networks to allow?
Anybus Defender 6004 uses a stateful firewall and the principle “what is not allowed is denied.” Communication is blocked unless it is explicitly permitted by the corresponding firewall rule.
How can I make only a specific PLC, HMI, or service inside a machine accessible?
Anybus Defender 6004 uses NAT and firewall rules to make only a selected device or network service accessible from the higher-level network without exposing the entire machine network.
How can I create firewall rules based on actual network communication?
In Anybus Defender 6004, rules can be created manually or directly from communication recorded in the firewall logs. The One-Click Easy Rule feature allows a corresponding firewall rule to be created quickly from a selected log entry.
How can I find out which network communication is actually required for machine operation?
Anybus Defender 6004 allows recorded communication to be monitored in the firewall logs and rules to be created from it. The Anybus Defender 6004 DPI/FW and PRO/FW variants additionally include an industrial traffic analyzer with automatic learning, which makes it easier to create more detailed rules.
How can I find out which devices are connected to the OT network?
Anybus Defender 6004 includes the Asset Discovery & Inventory feature, which discovers and identifies devices in the OT network. Depending on the available information, it can identify details such as the manufacturer, device type, software version, or update level. The feature is available in all three Anybus Defender 6004 variants.
How can I create multiple isolated networks without using a separate firewall for each one?
Anybus Defender 6004 supports VLANs. In addition to physically isolated segments, additional logically isolated networks can therefore be created, with dedicated communication rules configured between them.
Remote access and VPN
How can I provide secure remote access to machines and production networks?
The Anybus Defender 6004 DPI/FW and Anybus Defender 6004 PRO/FW variants can be used for secure remote access via VPN. Anybus Defender can operate as an OpenVPN server for connecting a service computer or other devices, while the PRO/FW variant also provides additional advanced VPN options for connecting remote networks.
How can I use an industrial firewall as my own OpenVPN server?
Anybus Defender 6004 in the DPI/FW and PRO/FW variants can operate as an OpenVPN server. It creates a secure VPN network that computers or remote devices can connect to and then access permitted parts of the production network.
How can I connect an industrial firewall with Ewon Flexy or Cosy for a private VPN network?
Ewon Flexy or Cosy can be connected as an OpenVPN client to the OpenVPN server in Anybus Defender 6004 DPI/FW or Anybus Defender 6004 PRO/FW. This makes it possible to create a private secure VPN infrastructure for remote access to machines and devices behind the Ewon.
How can I access a PLC or another device behind a remote gateway via VPN?
Anybus Defender 6004 can route communication from the VPN to networks and devices behind a remote gateway. Routing and firewall rules can be used to restrict access to only the required networks, devices, and services.
How can I allow a remote technician access only during a service period?
Anybus Defender 6004 allows rules to be scheduled by date, time, or duration. Selected communication can therefore be permitted only during the planned service intervention and remain blocked outside this period.
Configuration and management
How is Anybus Defender 6004 configured?
Anybus Defender 6004 is configured through the integrated web interface directly in a web browser, so there is no need to install separate configuration software. Setup wizards, firewall logs, and diagnostic tools are available.
How can I manage multiple Anybus Defender industrial firewalls from one place?
Multiple Anybus Defender devices can optionally be managed through the central Anybus Cybersecurity Console platform.
How can I integrate an industrial firewall into a higher-level system?
Anybus Defender 6004 provides a REST API for integration with higher-level systems. It also supports system logs and notifications via email, Syslog, Telegram Messenger, and Pushover.
Is the Anybus Defender 6004 license time-limited?
No. The Anybus Defender 6004 NAT/FW, DPI/FW, and PRO/FW variants are supplied with a perpetual license.
Highlighted items are mandatory.