

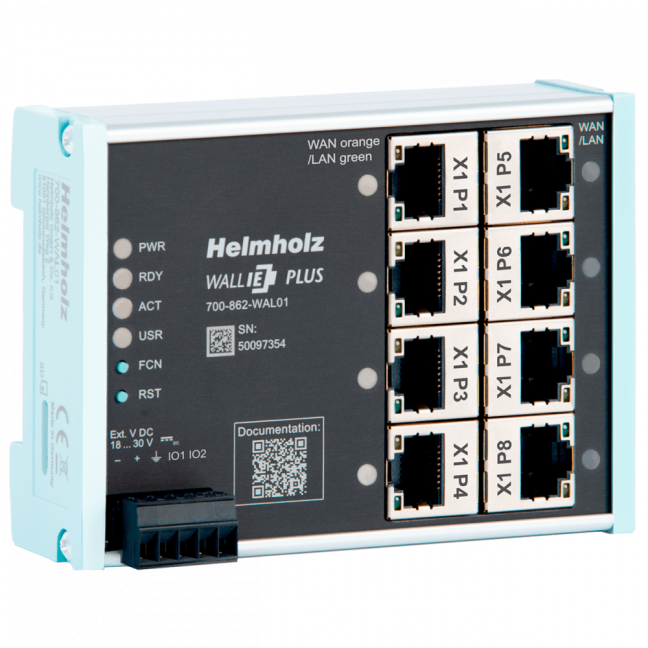
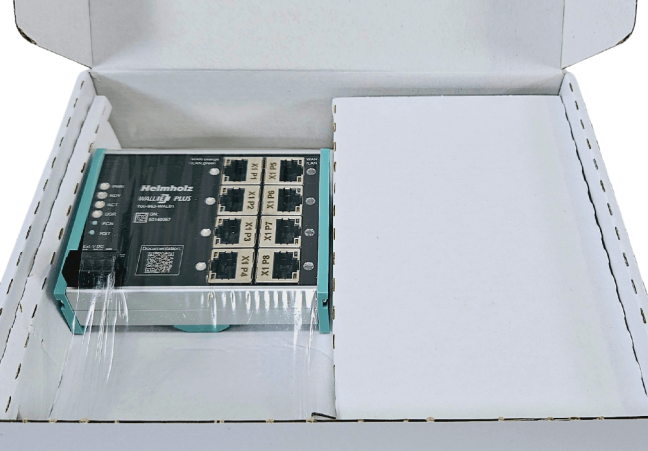


WALL IE PLUS, industrial Firewall, Ethernet Bridge and NAT router

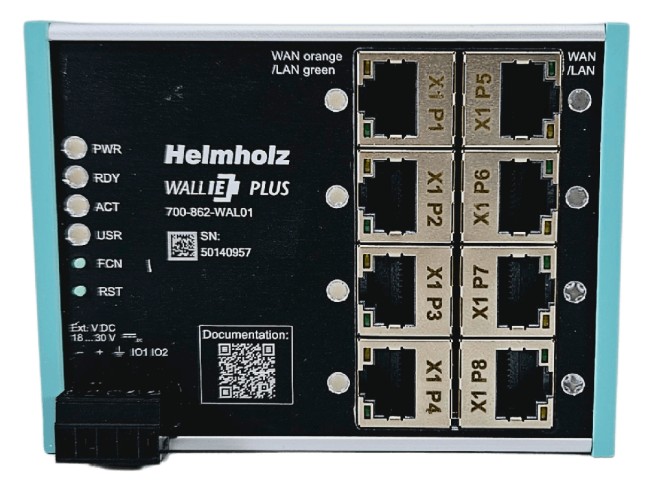
WALL IE PLUS is an industrial NAT gateway, Ethernet bridge and firewall for connecting a machine network to the company network. It provides 8 RJ45 ports operating at 100/1000 Mbit/s, individually assignable to WAN or LAN. It supports Basic NAT, NAPT, SNAT and rule-based traffic filtering. More
Code: HEL 700-862-WAL01
WALL IE PLUS is an industrial NAT gateway, Ethernet bridge and firewall for connecting a machine network to the company network. It provides 8 RJ45 ports operating at 100/1000 Mbit/s, individually assignable to WAN or LAN. It supports Basic NAT, NAPT, SNAT and rule-based traffic filtering. More
Code: HEL 700-862-WAL01
WALL IE PLUS - industrial NAT gateway and firewall
WALL IE PLUS (700-862-WAL01) connects the machine and company Ethernet networks and lets you define which traffic can pass between them. It has 8 RJ45 ports operating at 100/1000 Mbit/s, individually assignable to WAN or LAN. In NAT mode it translates IPv4 addresses; in Bridge mode it filters traffic between segments of the same IP network. This allows machines with identical addressing to be connected without changing their internal IP addresses.
Selection and ordering WALL IE PLUS
Send us the required quantity and a description of the connections. We will check availability and suitable accessories.
WAN and LAN port assignment
The eight ports of WALL IE PLUS are assigned to two groups: WAN for the company network and LAN for the machine network. At least one port must be assigned to each group. Ports within the same group are internally switched together. By default, port P1 is assigned to WAN and ports P2 to P8 to LAN.
Basic NAT and NAPT
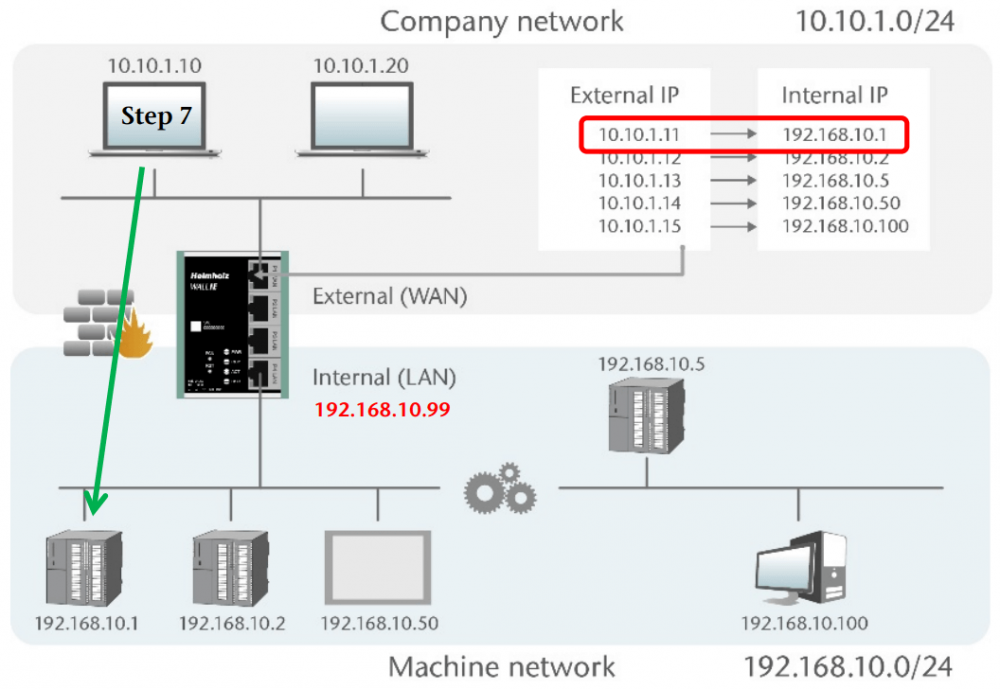
Basic NAT maps an internal machine IP address to a corresponding address in the external network. NAPT combines address translation with port numbers. Separate firewall rules for WAN-to-LAN and LAN-to-WAN traffic control access to individual devices.
This is useful for collecting data from several machines with the same IP addresses or connecting a machine subnet to a higher-level network. Address translation does not encrypt the transmitted data.
Address translation and permission to communicate are separate settings. After a Basic NAT rule is created, WAN-to-LAN access is blocked by default. Configure the corresponding firewall rules for the required connections. LAN-to-WAN traffic is permitted by default and can also be restricted by filters.

The IP addresses in the diagrams are examples. The illustrations show WALL IE Standard; refer to the Specifications tab for the number and arrangement of ports on the selected model.

Outgoing communication using NAPT
NAPT for LAN-to-WAN traffic replaces request source addresses with the WAN address of WALL IE and maps returning replies to the originating devices. For this communication, LAN devices must use the LAN address of WALL IE as their default gateway. This differs from the described WAN-to-LAN access with SNAT enabled, which does not require a change to the destination device default gateway.
SNAT without changing the machine default gateway
For permitted WAN-to-LAN connections, SNAT also replaces the source IP address with the LAN address of WALL IE. Devices in the machine network then send their replies directly to WALL IE. For these connections, the default gateway in the machine device does not need to be changed.

Bridge with traffic filtering
In Bridge mode, WALL IE operates as a layer 2 switch. It connects separate segments of the same IP network while allowing packets to be filtered according to rules. Access to part of the installation can therefore be restricted without introducing different IP subnets.

Port forwarding
Port forwarding redirects a request to a selected TCP or UDP port on the WAN interface to a specific device and port in the LAN. For example, access to 10.10.1.1:81 can be forwarded to 192.168.10.5:80. Configure the corresponding translation and firewall rules for each service.

Static routing
Static routes define the next gateway for destination subnets. They are used when a network that is not directly connected to WALL IE needs to be reached. The design must also provide a return path for replies.

Accessing SIMATIC S7 from STEP 7 and TIA Portal
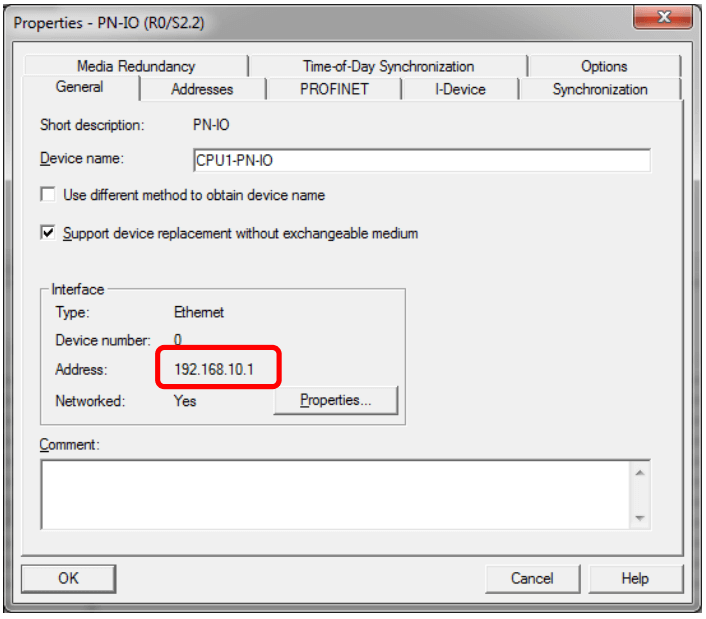
When accessing a PLC in the LAN from a computer in the WAN in Basic NAT mode, use the translated PLC address. Adapt the online connection in STEP 7 or TIA Portal to the address translation. Also ensure that replies return through WALL IE; depending on the connection, configure the PLC default gateway or use SNAT.
PROFINET RT frames are not forwarded between WAN and LAN. In NAT mode, broadcasts and multicasts are not forwarded between the interfaces either; in Bridge mode, ARP and DCP forwarding can be enabled. IP access to a PLC should therefore not be treated as a substitute for a transparent PROFINET RT connection.
In the described Basic NAT access scenario, PLC discovery using Accessible devices does not work. Enter the translated CPU address directly in the online access tool. With port forwarding through a single WAN address, the fixed TCP port 102 limits access from Simatic Manager or TIA Portal to one CPU.
Network and security functions
- Basic NAT, NAPT, port forwarding and SNAT for machine network integration.
- Separate WAN-to-LAN and LAN-to-WAN rules for IPv4 addresses, TCP/UDP ports and ICMP; MAC address filtering using allowlists or blocklists.
- Static routes, LAN DHCP server including static leases, and WAN DHCP client.
- LAN DNS server, time synchronisation via SNTP and time distribution to the LAN via NTP.
- FTP helper for active FTP in both NAT and Bridge modes.
- Web configuration via HTTPS with support for a custom certificate; by default, web interface access is restricted to the LAN.
- admin, it-user and machine-user accounts with different permissions; CFG configuration export and import.
- Syslog for system events and logins, with forwarding to an external Syslog server; current firmware also logs blocked packets.
- DIN rail mounting; IP20 protection.
Management by IT and maintenance teams
Configuration access can be divided between company network administrators and machine technicians. The admin account has full permissions. The it-user account accesses the device through WAN and has limited permissions, for example to configure the DHCP client, host name, certificate or remote Syslog server. Management access from WAN must be enabled separately.
The machine-user account accesses the device only through LAN and can change settings such as the DHCP server, NAT rules, packet and MAC filters, and static routes. Other settings are available to each restricted account according to its assigned permissions.
802.1X and current firmware
WALL IE supports the 802.1X supplicant role on the WAN side. It authenticates to the company network through a network device and an authentication server. 802.1X is not supported on the LAN side. Available methods include EAP-MD5, EAP-PWD, EAP-TLS, EAP-TTLS and PEAP.
The currently published firmware for WALL IE PLUS is V1.00.033. The 802.1X, NTP relay and extended logging functions are documented from version V1.00.033. Check the installed version on older devices first.
Export the configuration and schedule a maintenance window before updating. The update interrupts device operation; do not switch off the power supply during the update. Use the file intended specifically for this model.
Documentation and engineering
The Downloads tab contains the current V14 manual, V18 quick start guide, brochure, firmware, change history and STEP 3D models. Documents are labelled with their actual language. Manufacturer engineering macros are also available in the EPLAN Data Portal.
For deployment, restrict rules to the required connections, change default passwords and keep the firmware up to date. WALL IE forms part of network segmentation; the correct firewall configuration depends on the specific traffic used by the installation.
WALL IE is intended to separate the machine network from the company network. Internet connectivity must use a separate suitable router with an Internet firewall. WALL IE does not perform deep packet inspection (DPI) of permitted traffic; the allowed services and their use must follow the network design.
Device and connections
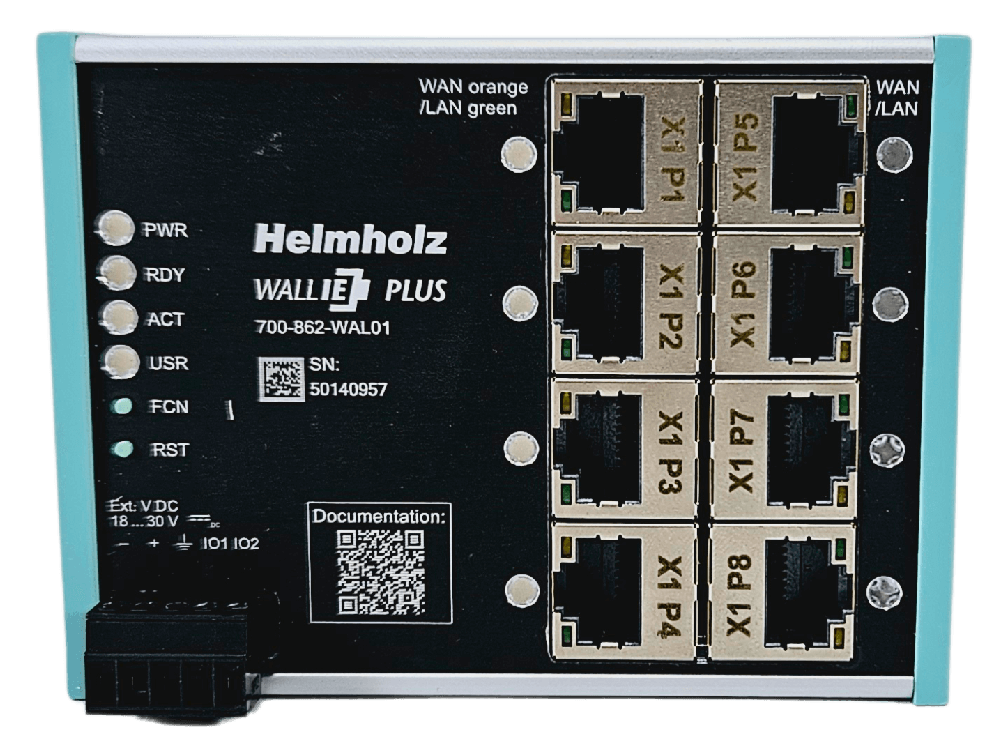


Why buy from FOXON
HELMHOLZ business partner
We are a business partner of HELMHOLZ. We supply new original products with a warranty.
Stock availability and delivery
We check current availability from our own and partner warehouses. Before you order, we confirm the price and possible delivery date for the specific model.
Product selection and technical advice
We help you choose the model, power supply and accessories to suit your connections and communication requirements.
Solution design and configuration
We discuss the connections and application requirements. Where needed, we propose a suitable setup and agree on the scope of assistance with configuration and commissioning.
Purchasing and technical advice
Selection and ordering WALL IE PLUS
Send us the required quantity and a description of the connections. We will check availability and suitable accessories.
WALL IE PLUS - technical specifications
| Manufacturer order number | 700-862-WAL01 |
|---|---|
| Device name | WALL IE PLUS |
| Scope of delivery | WALL IE PLUS, quick start guide |
| WAN / LAN | 8 RJ45 ports operating at 100/1000 Mbit/s, individually assignable to WAN or LAN |
| Ethernet connectors | RJ45 |
| Network modes | Bridge; NAT (Basic NAT, NAPT) |
| Address translation | Basic NAT, NAPT, port forwarding, SNAT |
| Traffic filtering | IPv4 addresses, TCP/UDP ports, ICMP; separate WAN-to-LAN and LAN-to-WAN rules; MAC address lists |
| Static routing | Yes |
| DHCP | LAN server including static leases; WAN client |
| DNS | LAN server |
| Time | SNTP client; LAN NTP server; NTP relay from V1.00.033 |
| 802.1X | WAN supplicant; no LAN support for 802.1X; from firmware V1.00.033 |
| EAP methods | EAP-MD5, EAP-PWD, EAP-TLS, EAP-TTLS, PEAP |
| Management | Responsive HTTPS web interface; custom certificate; default access from LAN only |
| User accounts | admin, it-user, machine-user |
| Configuration | CFG import and export; one active configuration |
| Logging | Syslog, external Syslog server; blocked packet logging from V1.00.033 |
| Current firmware | V1.00.033 |
| Manual | V14, 08.04.2026; also check the firmware history for new functions |
| PROFINET RT between WAN and LAN | Not supported |
| Broadcast and multicast | Not forwarded between WAN and LAN in NAT mode; ARP and DCP can be enabled in Bridge mode |
| FTP helper | Active FTP in both NAT and Bridge modes |
| Digital inputs | 2; 24 V DC to DIN EN 61131-2, type 2; no function in current firmware |
| Status LEDs | 4 for device status; 8 for port assignment; 16 for Ethernet |
| Supply voltage | 24 V DC; range 18-30 V DC; SELV/PELV |
| Current draw | Max. 275 mA at 24 V DC |
| Power dissipation | Max. 6,7 W |
| Operating temperature | 0 to +60 °C |
| Transport and storage | -40 to +85 °C |
| Relative humidity | Up to 95 %, non-condensing |
| Pollution degree | 2 |
| Protection rating | IP20 |
| Mounting | DIN rail; any mounting position |
| Dimensions (depth × width × height) | Manufacturer confirmation required: product page 34,5 × 101,5 × 75,5 mm; DE manual V14 34,5 × 101,5 × 76,5 mm; EN manual V14 32,5 × 101,5 × 76,5 mm. Verify the dimensional drawing before mechanical design. |
| Weight | Approx. 230 g |
| Certifications | CE |
| RoHS / REACH | Yes / yes |
| Basic NAT capacity | Max. 128 entries |
| Port forwarding capacity | Max. 128 entries |
| Packet filter capacity | Max. 128 rules per direction: WAN to LAN and LAN to WAN |
For firmware-dependent functions, use the version shown in the table or later. The nominal port speed does not guarantee firewall throughput for every configuration.
Highlighted items are mandatory.