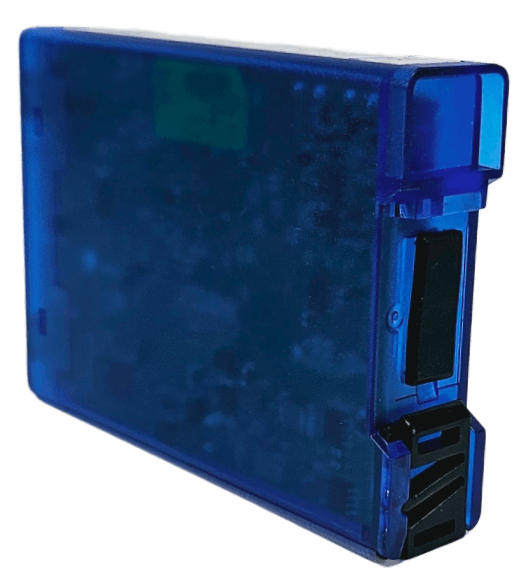
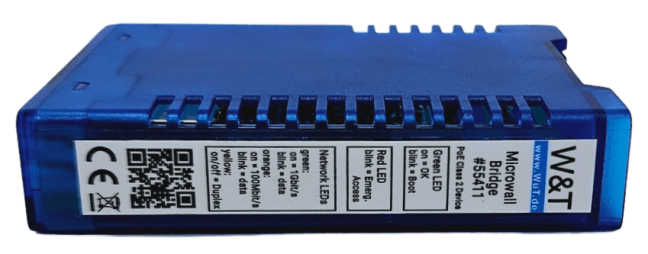
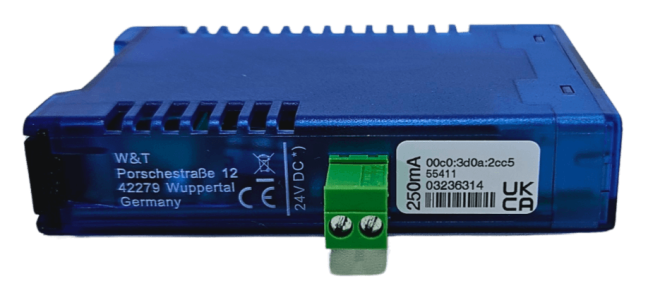


Microwall Bridge, průmyslový Firewall and Ethernet Bridge

The industrial network bridge will separate Ethernet devices in the same network range and the traffic between them will work according to the firewall rules. Data traffic can be unidirectional or bidirectional and communication is only between defined IP addresses, protocols and ports. More
Code: 55411
Firewall between devices whilst retaining IP addresses
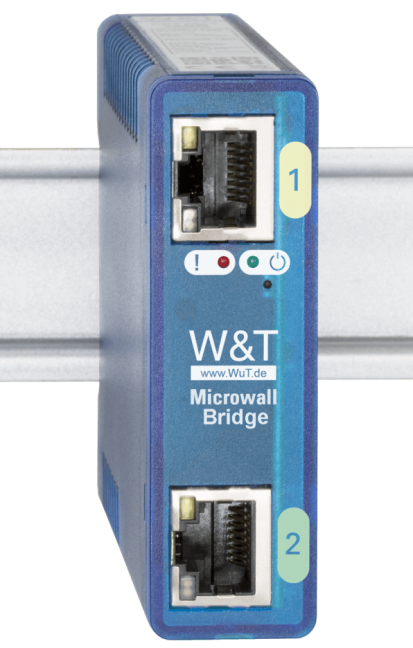
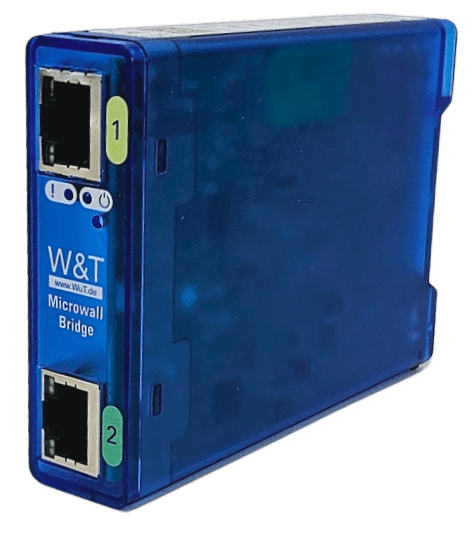
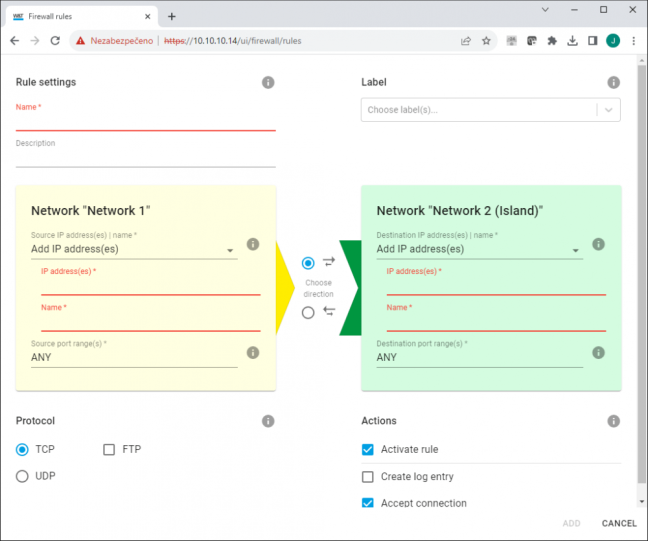
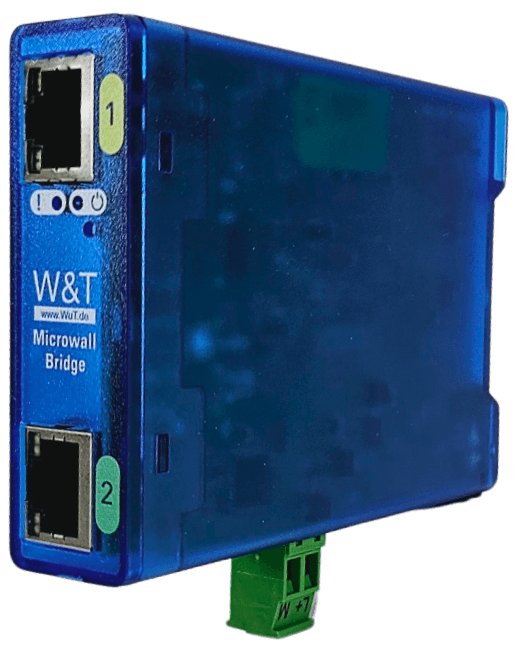
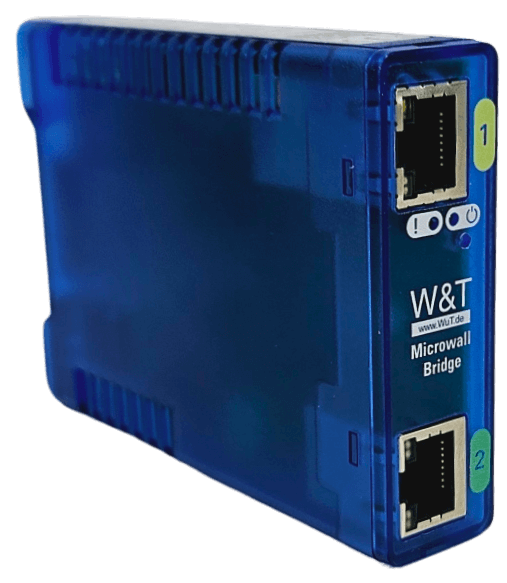
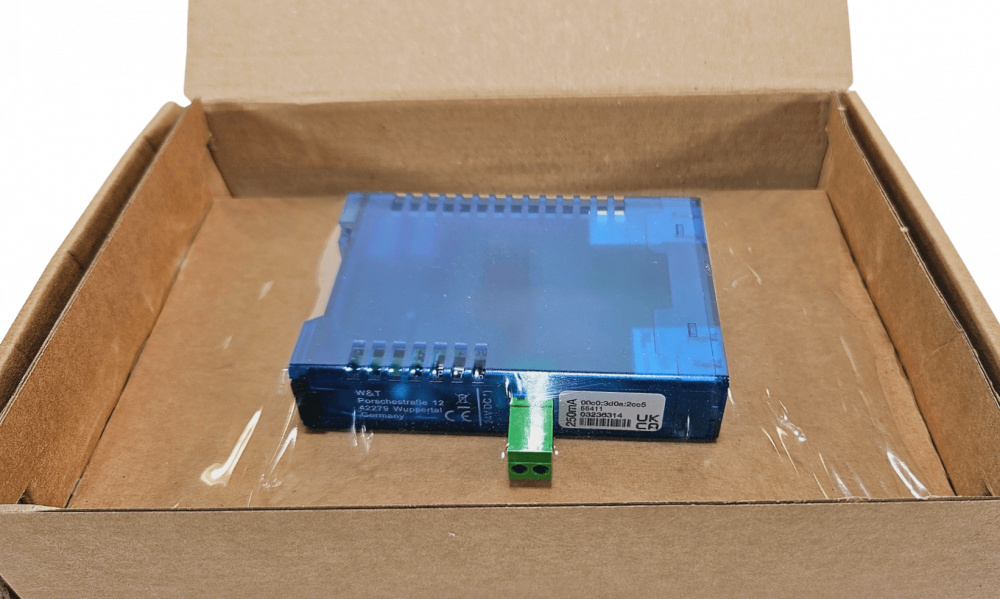
The W&T Microwall Bridge 55411 isolates communication between parts of an Ethernet network without changing the IP addresses of the connected devices. It operates as a transparent bridge with two Gigabit ports and a firewall that only allows explicitly authorised connections.
Do you need to select or order the W&T 55411?
Please send us the required quantity and a description of the wiring configuration. We will check availability and suitable accessories.
Usage
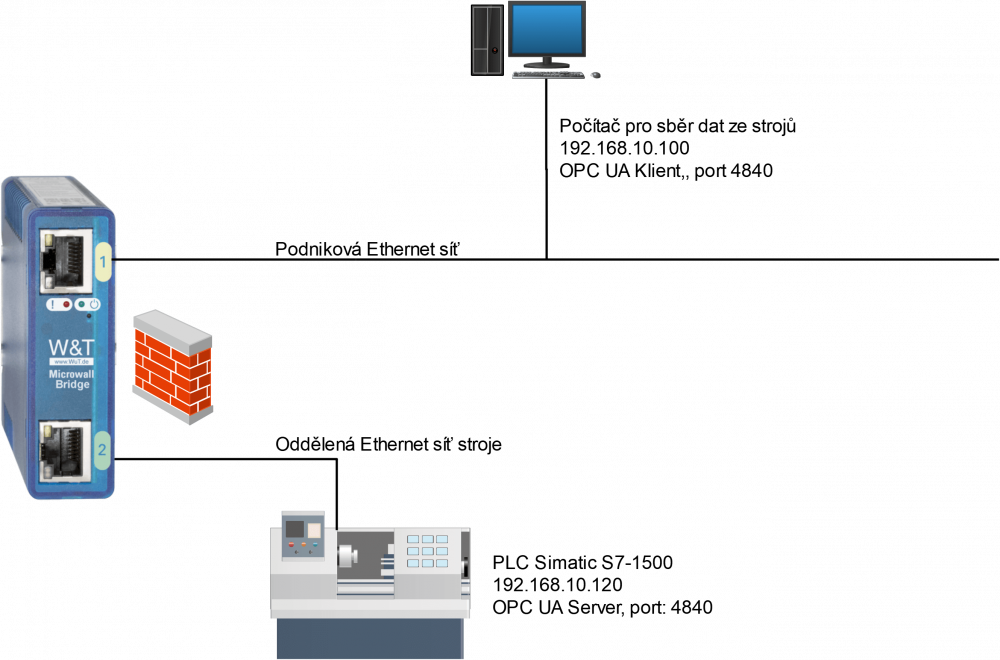
This is suitable for restricting communication by a machine or device within an existing network when it is necessary to retain the current IP configuration and routing. The rules are drawn up according to the services that are actually required.
Technical specifications for W&T 55411
| Network interface | 2x 100/1000BaseT with auto-detection/Auto-MDIX RJ45 IPv6 on request |
|---|---|
| Data throughput | max. 900 Mbit/s |
| Galvanic isolation | Network interface section: min. 1500 V |
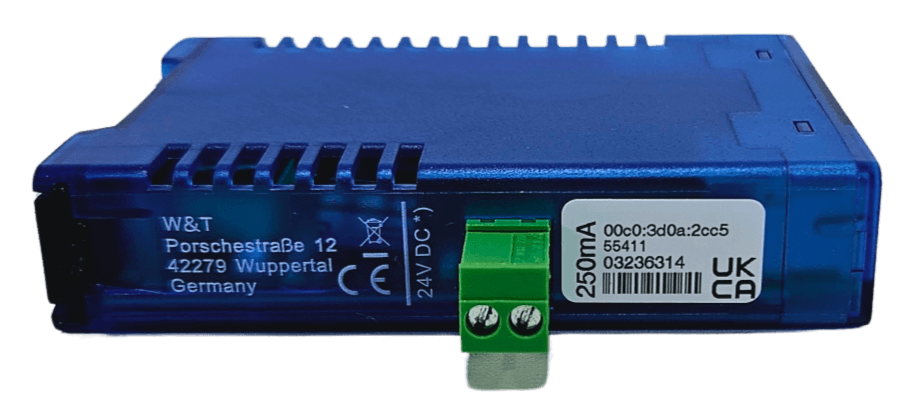
| Supply voltage | Power-over-Ethernet (PoE) or 24–48 V DC (±10 %) |
| Power connection | Removable screw terminal block, pitch 5.08 mm Marked ‘L+’ and ‘M’ |
| Current consumption | PoE Class 2 (3.84 W to 6.49 W) When using an external power supply: typ. 150 mA at 24 V DC max. 200 mA at 24 V DC |
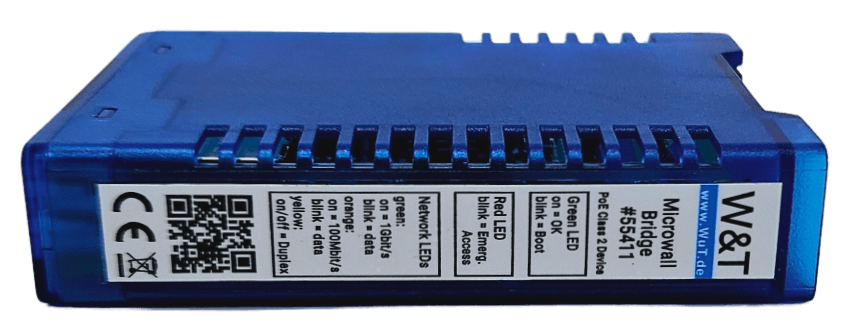
| Signalling | 2x LEDs for network status indication 1x LED for error indication |
| Housing and mounting | Compact plastic housing for DIN rail mounting 105 × 22 × 75 mm (length × width × height) |
| Degree of protection | IP20 |
| Weight | approx. 120 g |
| Ambient temperature | Storage: -40 to +85 °C Operating temperature 0 to +50 °C (when not installed in a stack) |
| Permissible relative humidity | 5 to 95 per cent RH, non-condensing |
| Contents of the delivery | 1x Microwall Bridge 1× quick start guide |
Network bridge and firewall rules
- Installing the bridge does not require any changes to the routing configuration or the IP addresses of protected devices. The Microwall Bridge is not an automatic replacement for a VPN router when designing a remote access solution.
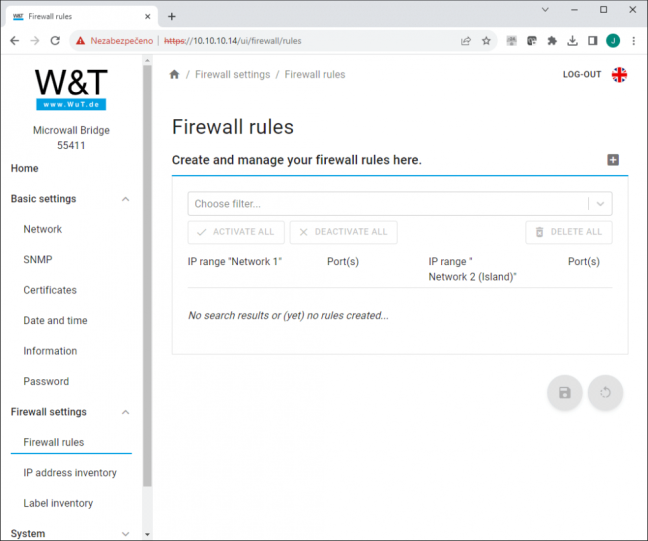
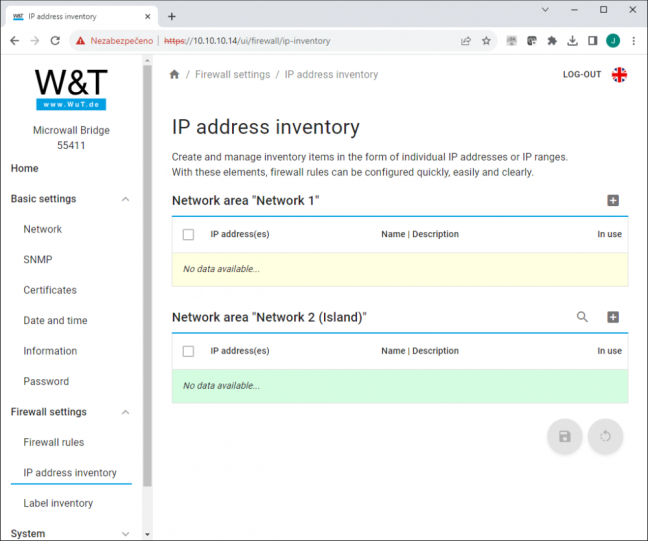
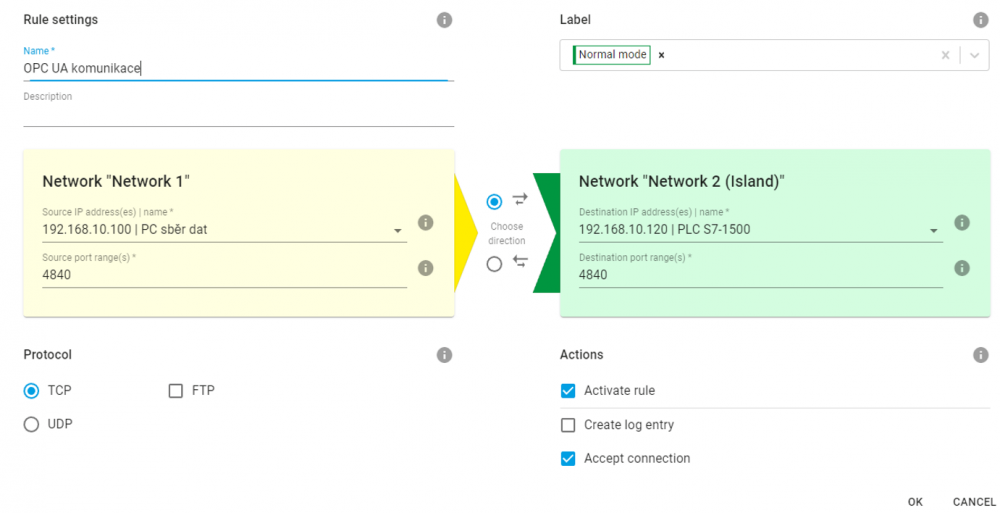
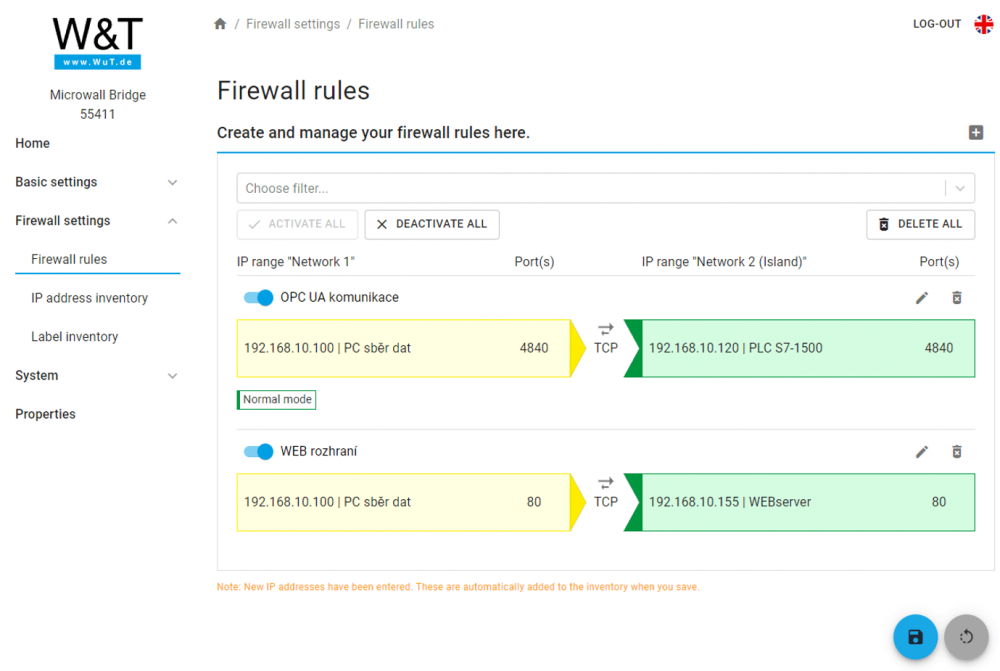
- Permitted communication is defined by IPv4 addresses and TCP/UDP ports. Unauthorised connection attempts can be logged and analysed.
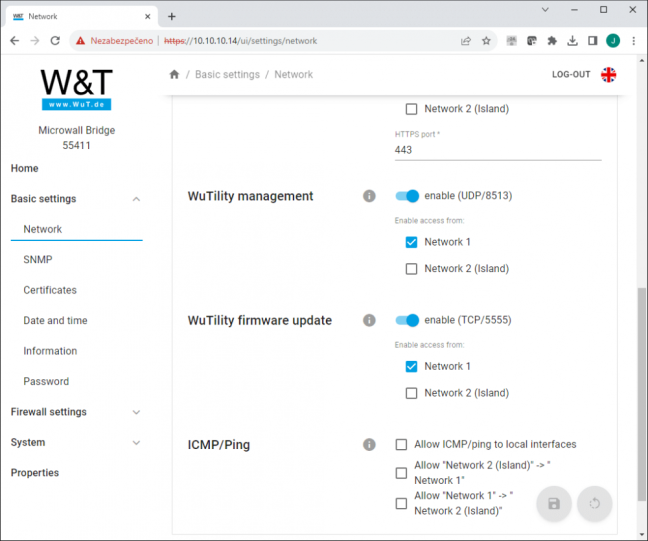
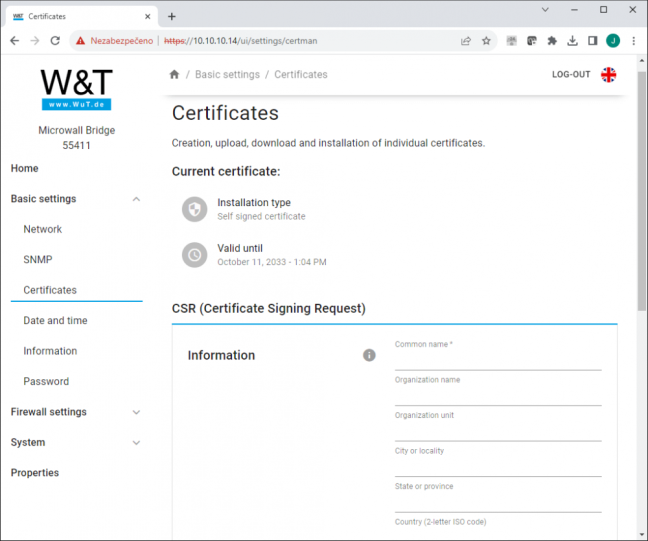
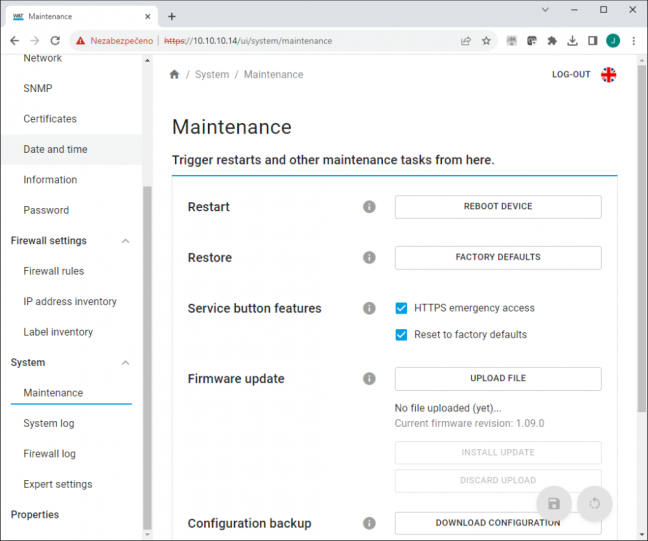
- The management system uses HTTPS and supports custom certificates. Secure Boot prevents the loading of tampered or unauthorised firmware. A password is set during initialisation; the default login is not used.
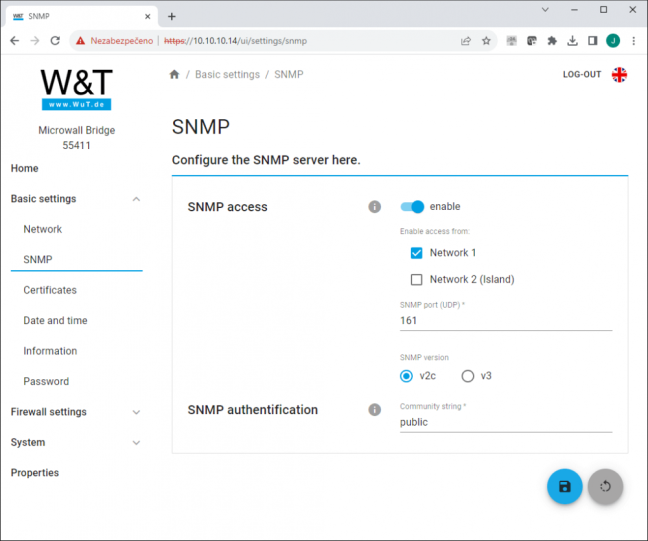
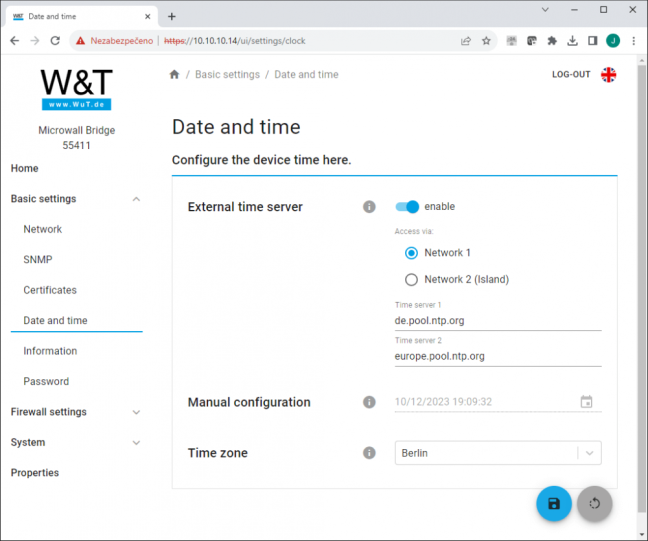
- Local services can be configured or disabled. Support for read operations via SNMPv2c/3 is listed as optional and requires verification for a specific request.
Commissioning and accessories
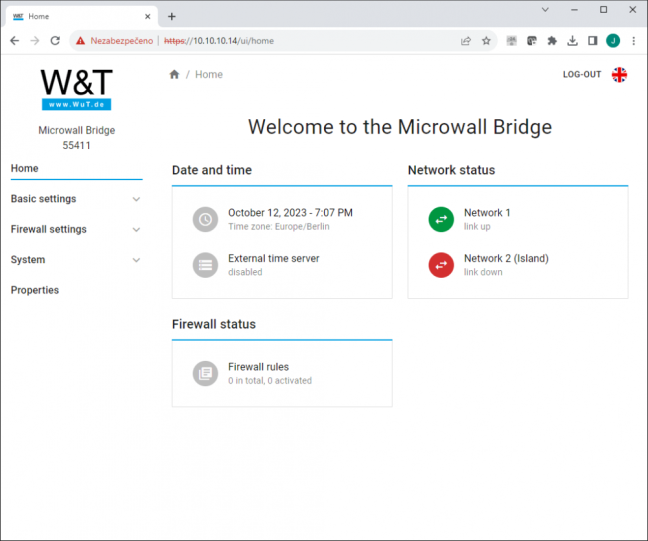
Familiarise yourself with the necessary communication relationships and set up the authorisation rules. Configure the management IP address, password and HTTPS access. Once connected to the network, test the authorised connections and verify that traffic is blocked as expected.
Contents of the delivery
- 1x Microwall Bridge
- 1× quick start guide
Frequently Asked Questions
Do I need to renumber the connected devices?
The transparent bridge is designed for deployment without changing the IP configuration of connected devices and without interfering with network routing.
Is WireGuard VPN part of this model?
This model is designed to function as a firewall bridge. For a router with WireGuard VPN, the corresponding Microwall VPN or Microwall IO models are available.
Will the device allow everything through simply by plugging it in?
Communication must comply with the defined authorisation rules. These rules must be prepared and verified before the system is put into operation.
Why order from FOXON?
Before placing an order, we will check the current availability of the part and confirm the estimated delivery date. We will assist you in selecting the equipment and necessary accessories based on the wiring configuration and required communication. We will confirm the warranty terms and the scope of any diagnostics or repairs for the specific quotation.
Documentation and technical consultancy
Technical data and documentation W&T 55411
Manuals, firmware and tools for this model can also be found in the Downloads tab. For service enquiries, please use sale and repair of FOXON industrial parts.
Do you need to select or order the W&T 55411?
Please send us the required quantity and a description of the wiring configuration. We will check availability and suitable accessories.
Diagrams and illustrations
Further related links
Technical specifications for W&T 55411
| Network interface | 2x 100/1000BaseT with auto-detection/Auto-MDIX RJ45 IPv6 on request |
|---|---|
| Data throughput | max. 900 Mbit/s |
| Galvanic isolation | Network interface section: min. 1500 V |
| Supply voltage | Power-over-Ethernet (PoE) or 24–48 V DC (±10 %) |
| Power connection | Removable screw terminal block, pitch 5.08 mm Marked ‘L+’ and ‘M’ |
| Current consumption | PoE Class 2 (3.84 W to 6.49 W) When using an external power supply: typ. 150 mA at 24 V DC max. 200 mA at 24 V DC |
| Signalling | 2x LEDs for network status indication 1x LED for error indication |
| Housing and mounting | Compact plastic housing for DIN rail mounting 105 × 22 × 75 mm (length × width × height) |
| Degree of protection | IP20 |
| Weight | approx. 120 g |
| Ambient temperature | Storage: -40 to +85 °C Operating temperature 0 to +50 °C (when not installed in a stack) |
| Permissible relative humidity | 5 to 95 per cent RH, non-condensing |
| Contents of the delivery | 1x Microwall Bridge 1× quick start guide |
How to Meet NIS2 Requirements: Secure Remote Access with Ewon Routers and W&T Firewalls
The European NIS2 directive introduces new obligations for companies in protecting against cyber threats. Below, we compare these requirements with the technical measures in IEC 62443 and show how to meet them easily using Ewon industrial routers, the secure Talk2M cloud service, and firewalls from the German manufacturer W&T.
Highlighted items are mandatory.
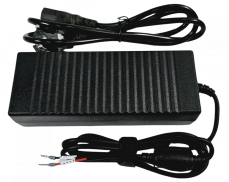
Power supply 24V 5A 120W
25,41 EUR Incl. VAT
Accessories1
Power supply 24V 5A 120W
25,41 EUR Incl. VAT